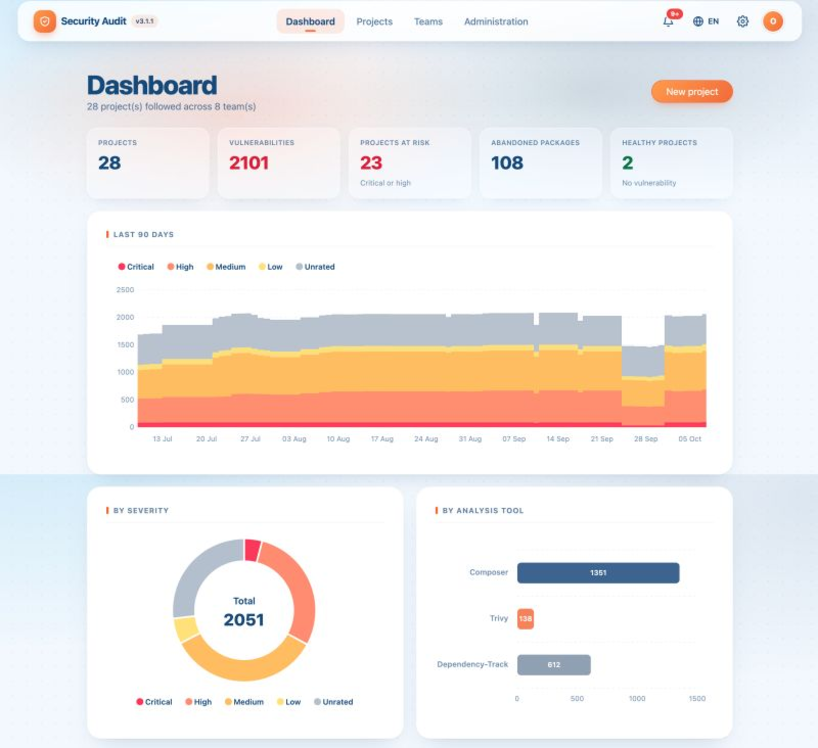
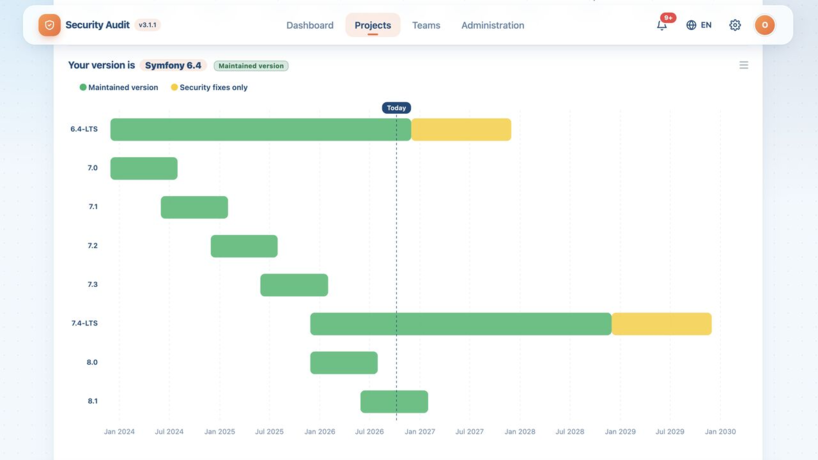


Security Audit, our tool for monitoring the health and security of your applications, is now at version 3.6. New design, new dashboard, new analyses and a detailed roadmap: the tool is moving fast, and it remains free.
A new design and a new dashboard
- A fully redesigned interface (v3.0), with a warmer theme with orange accents, carried over to the emails (v3.1).
- A vulnerability statistics dashboard per team, to see at a glance where to act first.
- Full-text search across your projects, and improved notifications that you can mark as read.
New analyses
Security Audit no longer stops at your dependencies: it also looks at how exposed your environments are.
- HTTP security headers of your environments, with ownership verification (v3.3).
- TLS and certificate analysis (v3.4).
- HTTP protocol analysis (v3.5), then a compression rule (v3.6.3).
- Your services' vulnerabilities are filtered by the versions actually affected.
More accurate results
- Support for the advisories you ignore in your composer.json .
- Updated severities and completed existing vulnerabilities.
A hardened tool
We audited Security Audit the way we audit your applications: CSRF protection on sensitive actions, rate limiting on login and the API, HSTS and CSP headers, two-factor authentication, and protections against SSRF and path traversal.
The roadmap
[TO COMPLETE: the next steps of the roadmap]
Still free
Monitoring the health and security of your applications shouldn't depend on your budget. Try the new version and tell us what you think.
Nos derniers articles
Security Audit gets a makeover: new design, new dashboard, still free
New dashboard, new design, new analyses and an ambitious roadmap: Security Audit moves to version ...
Code généré par IA, Shadow Dev et dette technique : comment éviter la déstabilisation de votre application PHP/Symfony ?
Si les assistants IA ont révolutionné la production de code en accélérant significativement le développement, ...
Nouveautés de Dataflow : stockage des logs en fichier, et nettoyage automatisé de l'historique
Vous en avez marre d'avoir les logs de vos jobs dans la base de données ...
Comment utiliser les paramètres avec ibexa_render et ibexa_render_location
Si vous développez sur Ibexa depuis quelques années, vous avez pris pour habitude de passer ...
Reprise de la maintenance du provider Apple pour PHP League OAuth2 Client
Code Rhapsodie reprend la maintenance du package oauth2-apple de Patrick Bussmann. Ce fork garantit la ...
Nouvelle fonctionnalité de suggestion de mots-clés au connecteur Gemini pour Ibexa
La suggestion de mots-clés de Taxonomy est disponible dans Ibexa DXP avec le pack de ...
Split a large SQL file into smaller ones for easier import
Importing a very large SQL file can be problematic, sometimes causing your virtual machine (VM) ...
Sylius vs Shopware : Quelle architecture choisir pour votre futur e-commerce ?
Sylius et Shopware sont deux outils (framework) permettant la réalisation d'un site e-commerce. Comment choisir ...
Ibexa announces the release of a new LTS version with contributions from Code Rhapsodie
Ibexa published a security advisory and subsequently released new versions of Ibexa DXP v4.6.26 and ...